
Your MDM admin just quit. What happens...
6 October 2026If your only mobile device management (MDM) admin just resigned, the next two weeks matter more than the hiring decision. Most of what keeps a fleet running lives in that…
Read more Canadian
MDM as a Service by PiiComm allows organizations to offload the complex administration of Mobile Device Management platforms to certified experts.
PiiComm managed mobility services can support your MDM needs. View our MDMaaS Guide for in-depth insights.
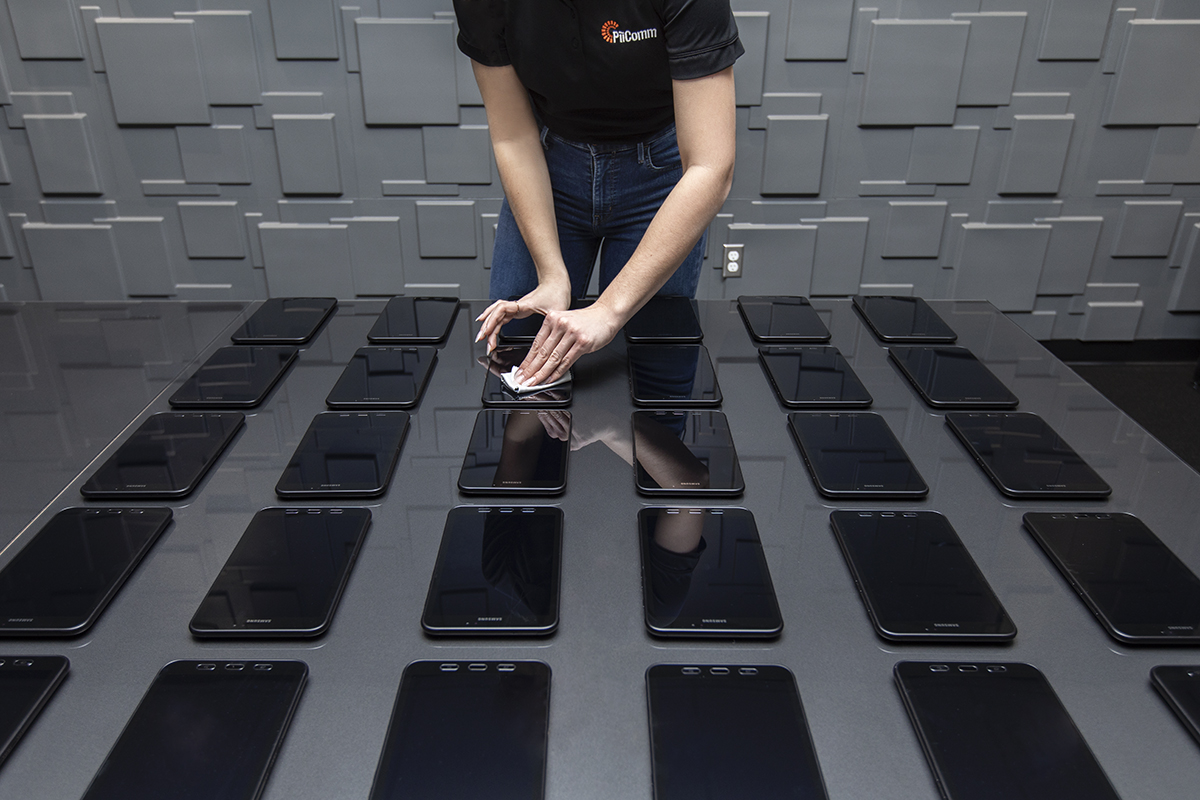
PiiComm’s MDM as a Service is a fully managed solution where our certified, Canada-based administrators handle the day-to-day operations of your Mobile Device Management environment.
Unlike basic software support, we take ownership of your policy configurations, application deployments, and security monitoring, ensuring your fleet remains compliant without burdening your internal IT resources.





Our Service Desk monitors device health metrics 24/7, identifying connectivity issues or battery failures before they impact field workers.
We enforce "Lockdown" policies to restrict non-business usage and remotely wipe lost devices to prevent data breaches.
PiiComm manages the testing and remote deployment of your business-critical apps, ensuring version consistency across the enterprise.
| Capability | PiiComm MDMaaS | Internal IT Administration |
|---|---|---|
| Expertise Level |
Certified MDM Architects (SOTI/VMware)
|
Generalist IT Staff
|
| Monitoring Coverage |
24/7/365 (Proactive Alerting)
|
Business Hours Only (9-5)
|
| Response Time |
SLA-Backed (Guaranteed Response)
|
Variable (Competing Priorities)
|
| Security Updates |
Immediate (Scheduled Execution)
|
Reactive / Delayed PATCHing
|
| Policy Complexity |
Granular Control (Role-Based Access)
|
Basic Profiles
|
| Cost Structure |
Predictable (Flat Monthly Fee)
|
Hidden (Staff Salaries + Training)
|
If your only mobile device management (MDM) admin just resigned, the next two weeks matter more than the hiring decision. Most of what keeps a fleet running lives in that…
Read morePiiComm differs from carrier, value-added reseller (VAR), OEM-direct, and in-house device management because it is a single Canadian-operated managed mobility services (MMS) provider accountable for the whole device lifecycle: sourcing,…
Read moreIf you have been briefed on “autonomous endpoint management” in the past year, here is the short version: the direction is real, the analysts have formalized it, and almost nothing…
Read moreIf you manage a mixed fleet of laptops, smartphones, and rugged handhelds, you have probably heard RMM and UEM used as though they mean the same thing. They don’t. RMM…
Read morePiiComm’s in-country MDM technicians are fully certified on all major enterprise MDM platforms, including SOTI MobiControl, VMware Workspace ONE (AirWatch), and Microsoft Intune. We support both on-premise and cloud-based deployments, providing a single point of expertise for diverse environments.
Yes. PiiComm specializes in complex MDM migrations (e.g., migrating from legacy on-prem to cloud). We manage the entire project lifecycle—from planning and profile replication to device re-enrollment—ensuring zero data loss and minimal operational disruption.
Our sovereign managed mobility services cover the complete lifecycle of digital management:
We provide proactive 24/7 monitoring to validate:
Most MDM comparisons are platform comparisons — Intune against SOTI against Workspace ONE. That is the second decision. The first is whether you are buying software your team will run, or a managed service where someone else runs it. Once that is settled, five criteria separate the options that work here from the ones that do not.
PiiComm's certified technicians administer your MDM environment as a managed service — including migration between platforms — with Canada-based administrators and 24/7/365 monitoring. The complete MDMaaS guide sets out the full evaluation framework.
Four tool categories do different parts of this job and are frequently confused. Mobile application management (MAM) controls corporate apps and data on a device you do not own — containerization, per-app policy, selective wipe. App vetting or reputation services assess what an app actually does: permissions, data flows, embedded SDKs, known vulnerabilities. Mobile threat defense (MTD) watches the device at runtime for malicious apps, network attacks and OS compromise. UEM app policy governs what can be installed at all. A BYOD programme usually needs MAM plus one of the other three, and which one depends on whether your real risk is unvetted apps, active threats, or simply unmanaged corporate data. PiiComm's technicians administer application management and policy enforcement as part of your MDM environment.